Data Encryption
All customer data is encrypted through industry-accepted standards: AES 256 for data at rest and TLS 1.2 or higher for data in transit.


Our approach
Demonstrating commitment to prioritizing and investing in robust security measures, Hypatos has established an independent security team, reporting directly to the CEO, to develop, implement, and maintain our security program. The team also collaborates closely with our customers, ensuring their specific security requirements are met, and provides guidance and best practices to our engineering and product teams.
Certified & Acknowledged
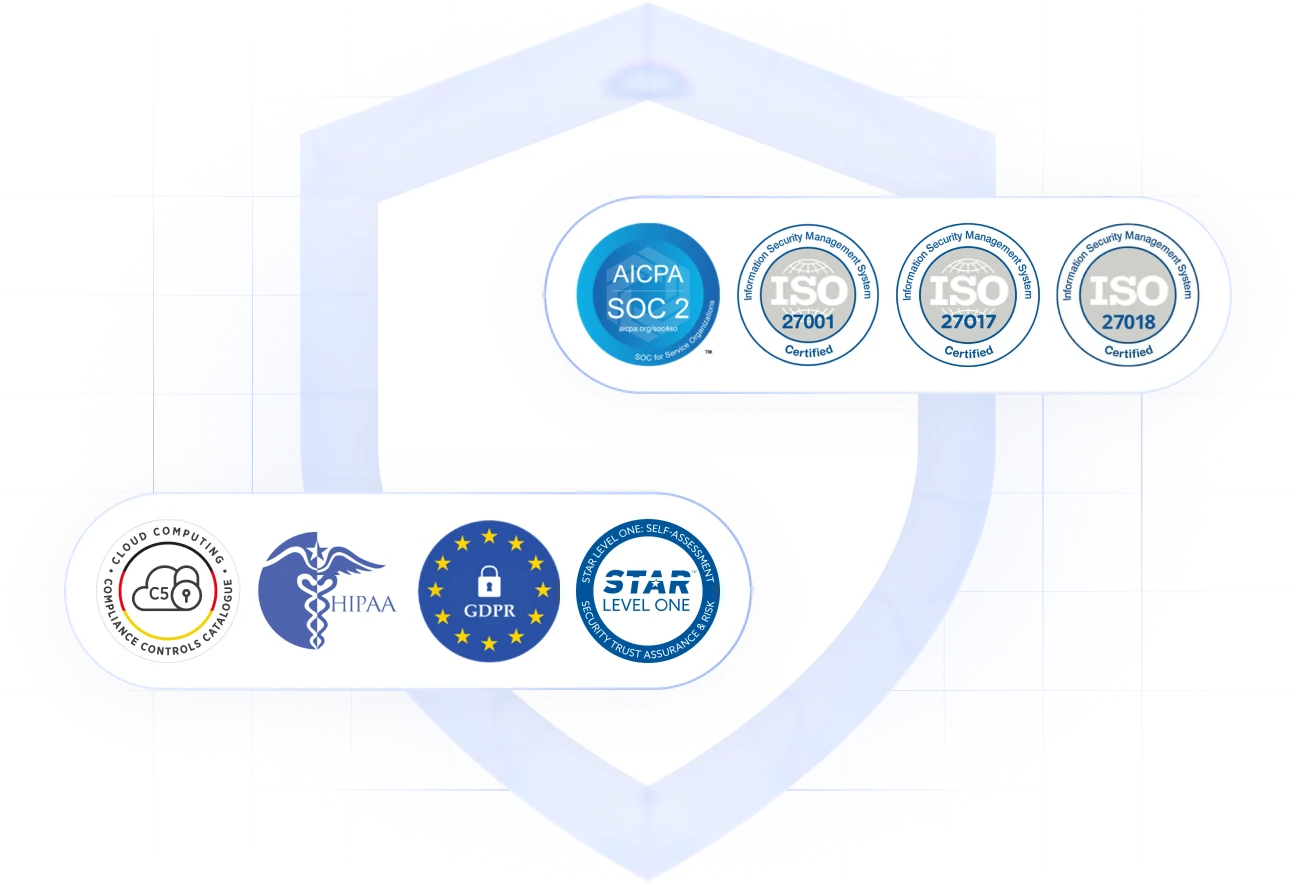
Hypatos is independently certified to SOC 2 Type 2, ISO 27001, ISO 27017, ISO 27018, and BSI C5, and is compliant with HIPAA and GDPR.
Our cloud services are in the STAR Level 1 Registry by the CSA, and Hypatos has its own CAIQ version. The CAIQ documents security controls in cloud services, promoting transparency and helping customers evaluate SaaS security. All audit reports and certificates are in our Trust Center.

All customer data is encrypted through industry-accepted standards: AES 256 for data at rest and TLS 1.2 or higher for data in transit.
We conduct annual third-party penetration tests covering the top 10 OWASP security risks. Summary reports are in our Trust Center.
At Hypatos, we prioritize AI security by following the OWASP Top 10 Risks for LLM Applications 2025. This ensures protection against threats and safeguards data integrity.
Do you have a question? Don’t hesitate to contact our security team on security@hypatos.ai
